When most people think about executive protection and event security, they picture security professionals accompanying an executive, monitoring an entrance, or managing access to a venue. While these responsibilities are important, they represent only a portion of an effective security operation.
The most successful security assignments often depend on work completed well before personnel arrive on-site or an event opens its doors.
This preparation, commonly known as security advance work, involves evaluating potential threats, assessing locations, reviewing logistics, coordinating with stakeholders, and developing plans to address foreseeable risks. It helps transform security from a reactive function into a proactive, risk-informed operation.
For organizations hosting high-profile executives, corporate meetings, conferences, and special events, advance planning can make the difference between a coordinated security program and one that struggles to respond when circumstances change.
At Premier Risk Solutions, effective security begins with understanding the assignment, identifying potential vulnerabilities, and preparing the people and processes needed to manage risk.
What Is Security Advance Work?
Security advance work is the process of evaluating an upcoming assignment or location before the primary security operation begins. It helps security teams understand the environment, identify potential vulnerabilities, and establish procedures that support safe and efficient operations.
The scope varies depending on the assignment. Protecting a corporate executive traveling between multiple locations requires a different approach from securing a large conference, private corporate gathering, or public-facing executive appearance.
However, the underlying objective remains consistent: identify foreseeable challenges before they become operational problems.
Reviewing the client’s objectives, itinerary, and operational requirements.
Conducting venue and site assessments.
Evaluating access control, visitor management, and perimeter security.
Assessing transportation arrangements and relevant logistical dependencies.
Coordinating with client security teams, venue management, and other stakeholders.
Reviewing emergency procedures and available response resources.
Identifying contingencies for changing conditions, disruptions, or unexpected incidents.
The outcome should be a practical security plan that reflects the actual operating environment, not simply a generic checklist.
1. Executive Protection Begins With Preparation
Executive protection is frequently associated with close protection personnel accompanying a principal. However, the effectiveness of a protection detail depends on much more than the presence of a security professional.
Executives travel between offices, hotels, restaurants, conference centers, airports, and other locations where the security environment can change throughout the day. Each transition introduces different considerations involving access, transportation, privacy, timing, and coordination.
Advance planning helps security teams understand these environments before the executive arrives.
Understanding the operating environment
An effective advance considers the locations an executive is expected to visit, the operational requirements of each stop, and the procedures necessary to support secure and efficient movement.
This can include reviewing venue access arrangements, confirming designated contacts, identifying appropriate entry and exit options, and understanding the site’s emergency procedures.
For business travel, coordination with transportation providers, executive assistants, and corporate security personnel can also reduce uncertainty and help prevent avoidable disruptions.
Planning for contingencies
Schedules change. Meetings run late. Transportation arrangements become unavailable. Venues experience unexpected operational issues.
Security plans should account for reasonable contingencies rather than assume every part of an itinerary will proceed as expected.
Establishing communication protocols, identifying decision-makers, and preparing alternative arrangements helps teams respond more effectively when circumstances change.
The goal is not to eliminate every possible risk. It is to reduce uncertainty, improve coordination, and ensure the team is prepared to make informed decisions.
2. Event Security Is Determined Long Before the Doors Open
Corporate events create a different set of security challenges. Conferences, executive meetings, product launches, award ceremonies, and private gatherings may bring together employees, clients, senior leaders, vendors, contractors, and members of the public.
These activities can involve multiple access points, complex schedules, temporary infrastructure, and competing operational priorities.
Security planning must account for these factors without unnecessarily interfering with the attendee experience.
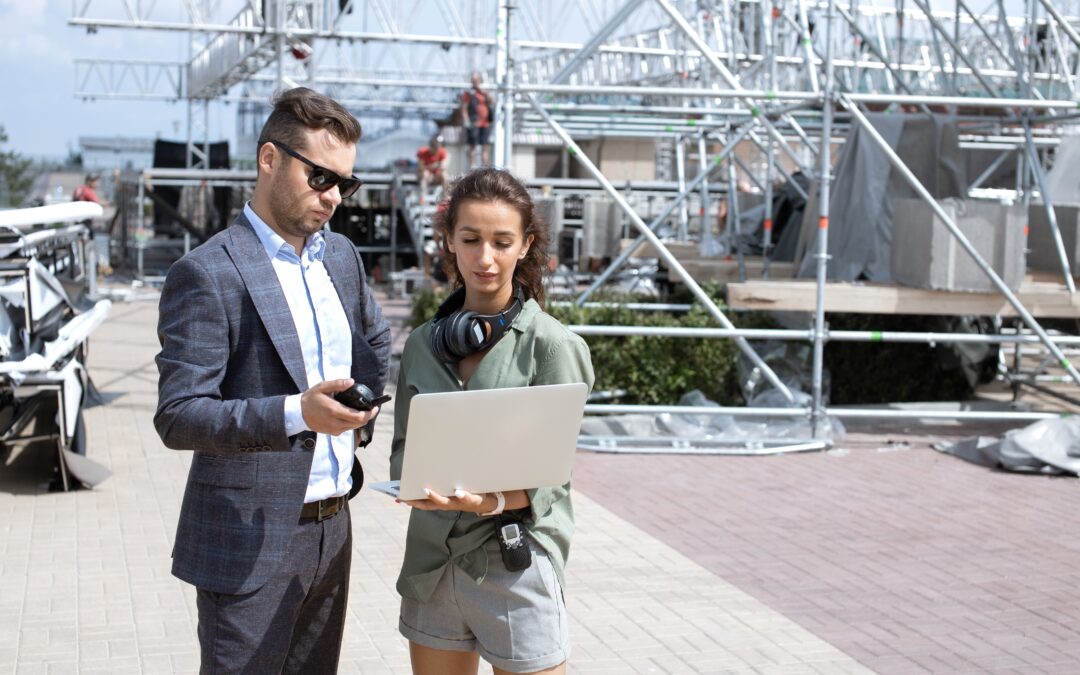
Assessing the venue
A venue walkthrough provides an opportunity to understand how the site functions and how security procedures should support its layout and intended use.
Depending on the event, an assessment may examine:
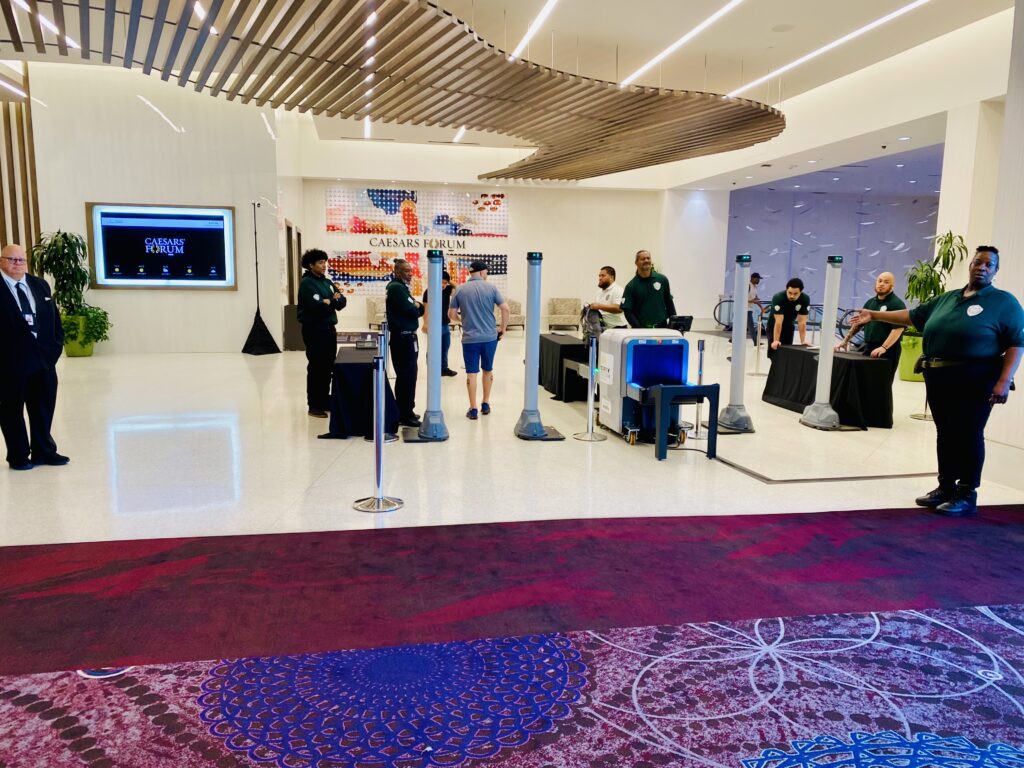
Entrances, exits, and visitor screening arrangements.
Credentialing procedures and restricted-access areas.
Loading docks, service corridors, and vendor access.
Emergency exits and evacuation procedures.
Security staffing requirements and post responsibilities.
Communications systems and escalation procedures.
Coordination between venue personnel, event organizers, and security teams.
A venue that works well for an ordinary business meeting may require additional planning when hosting a high-profile executive or a large gathering with heightened security requirements.
The objective is to identify gaps early enough that they can be addressed during planning rather than during the event itself.
Integrating security with event operations
Security should not operate independently of the event team.
Event organizers need to understand how security procedures affect registration, guest movement, deliveries, schedules, and the overall attendee experience. Security personnel, in turn, need timely information about changes that could affect their responsibilities.
Establishing clear points of contact, reporting procedures, and escalation protocols before the event helps reduce confusion and supports consistent decision-making.
When security is incorporated into event planning from the beginning, it becomes easier to balance protection, professionalism, and operational efficiency.
3. Risk Assessments Turn Observations Into Action
A site visit alone does not constitute a complete security advance. Observations must be evaluated, prioritized, and translated into practical recommendations.
A structured risk assessment helps organizations distinguish between issues that require immediate attention and those that can be addressed through longer-term improvements.
What could happen? Identify credible threats, operational vulnerabilities, and foreseeable disruptions relevant to the assignment.
What would the consequences be? Consider potential impacts on personnel safety, business continuity, assets, reputation, and the successful completion of the event or visit.
What should be done about it? Recommend proportionate controls, assign responsibilities, and establish procedures for addressing identified risks.
Not every vulnerability requires additional security personnel or expensive technology. Some issues can be mitigated through better access procedures, improved communication, revised scheduling, clearer responsibilities, or more effective coordination.
This distinction matters because the objective is not to maximize security spending. It is to allocate resources where they provide meaningful risk reduction.
For organizations evaluating their existing programs, independent physical security consulting can provide an additional perspective on whether current procedures adequately address operational needs.
4. Coordination Is as Important as Equipment and Personnel
Even a well-designed security plan can fail when responsibilities are unclear or critical information does not reach the people who need it.
Executive protection and event security frequently involve several parties, each responsible for different elements of the operation. These may include corporate security teams, executive assistants, facilities personnel, venue management, transportation providers, event organizers, and external security contractors.
Advance work establishes how these parties will communicate and coordinate.
Before an assignment begins, teams should understand:
Who has authority to make operational decisions.
Who receives and distributes time-sensitive information.
How incidents and emerging concerns should be reported.
Which party is responsible for each security function.
How schedule changes and operational disruptions will be communicated.
What procedures apply when an issue requires escalation.
These arrangements are especially important when multiple organizations share responsibility for a location or event.
Clear communication does not eliminate the possibility of an incident. It helps reduce avoidable confusion and improves the likelihood that personnel will respond consistently when something unexpected occurs.
5. Contingency Planning Helps Teams Adapt
No advance can predict every development. Weather, transportation disruptions, medical emergencies, schedule changes, technical failures, and unexpected security concerns can affect even carefully planned assignments.
The purpose of contingency planning is to establish reasonable alternatives and decision-making procedures before they are needed.
For executive protection, this may involve confirming alternative transportation arrangements, establishing communication protocols, or understanding the procedures available if a scheduled location becomes unavailable.
For event security, contingencies may address medical response, evacuation, severe weather, access-control failures, crowd-management issues, or changes to the event schedule.
Plans should be proportionate to the assignment and coordinated with the organizations responsible for implementing them.
Personnel should also understand their individual responsibilities. A written emergency plan has limited value if the people expected to carry it out have not reviewed it or do not understand how their roles fit into the broader response.
Where appropriate, briefings, tabletop exercises, and practical rehearsals can help validate procedures and identify gaps before the assignment begins.
6. Advance Work Supports Better Business Outcomes
Security planning is often viewed primarily as a protective measure. However, effective preparation can also support business objectives.
For corporate leaders, an avoidable security disruption may affect schedules, stakeholder confidence, employee safety, and the organization’s reputation. At a corporate event, operational confusion can undermine the attendee experience and place unnecessary pressure on event staff.
Advance work helps organizations address these concerns before they interfere with the intended outcome.
Potential benefits include:
Reduced operational uncertainty: Teams have a clearer understanding of responsibilities, procedures, and contingencies.
More effective resource allocation: Security personnel and other resources can be assigned according to identified risks and operational requirements.
Improved coordination: Stakeholders have defined communication channels and escalation procedures.
Greater operational continuity: Teams are better prepared to manage foreseeable disruptions.
More informed decision-making: Security recommendations are based on observed conditions and assignment-specific requirements.
These benefits should be evaluated against the needs of each operation. While it is difficult to quantify every incident prevented through planning, organizations can measure practical indicators such as completion of advance assessments, closure of identified vulnerabilities, briefing completion, response readiness, and adherence to established procedures.
The result is a more deliberate approach to security investment, with decisions grounded in operational requirements rather than assumptions.
7. Why Organizations Benefit From Experienced Security Partners
Internal security teams understand their organizations, personnel, and business priorities. External security partners can complement that knowledge by providing additional operational experience, independent assessment, and specialized support when required.
The value of a security partner is not simply the ability to supply personnel. It is the ability to understand the assignment, identify relevant risks, coordinate with existing stakeholders, and translate requirements into an executable plan.
For organizations with established internal security programs, an experienced partner should work collaboratively with existing leadership rather than create unnecessary duplication.
For organizations without dedicated security resources, professional support can help establish appropriate procedures and identify where additional capabilities may be needed.
The right approach depends on the assignment, the organization’s existing capabilities, and its risk profile. In each case, advance planning provides a foundation for a more coordinated and purposeful security operation.
Conclusion: The Best Security Work Often Happens Before Anyone Notices It
Successful executive protection and event security are not defined solely by what happens on the day of an assignment. They are shaped by the preparation, coordination, and decision-making that occur beforehand.
A thorough advance helps security teams understand their environment, identify vulnerabilities, establish responsibilities, and prepare for foreseeable challenges. It also helps organizations align security requirements with their operational objectives.
For businesses hosting executives, managing high-profile events, or coordinating complex security assignments, this preparation should be treated as a core component of the security strategy—not an optional administrative step.
At Premier Risk Solutions LLC, effective security starts with understanding the client’s needs and preparing for the realities of the assignment.
Planning an executive visit, corporate event, or complex security operation? Premier Risk Solutions LLC can help your organization evaluate its requirements and develop a coordinated approach to executive protection, event security, and advance planning.
Contact Premier Risk Solutions LLC to discuss your security requirements and learn how professional planning can support your next assignment.
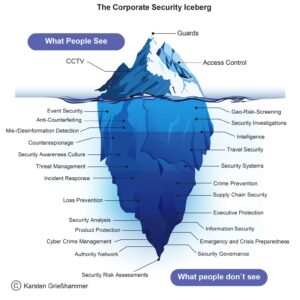
When executives think about corporate security risks, they often focus on the most visible threats: workplace violence, theft, unauthorized access, cyberattacks, or physical intrusion. While these threats deserve serious attention, some of the most significant security vulnerabilities facing organizations can be much less obvious.
Security gaps often develop between departments, processes, people, facilities, vendors, and technology. An organization may have security policies, access-control systems, surveillance cameras, security personnel, and emergency procedures, yet still maintain vulnerabilities that could expose employees, executives, facilities, clients, and business operations.
For executives, understanding every technical aspect of security isn’t necessarily the objective. The more important question is whether leadership understands where the organization’s greatest security exposures exist—and whether those risks have been properly evaluated.
At Premier Risk Solutions, we believe effective security begins with understanding an organization’s risk environment, identifying vulnerabilities, and developing practical strategies to reduce exposure before a security incident occurs.
Here are five security risks executives often overlook.
1. Security Gaps Created by Business Growth
Business growth is a positive development, but it can also create new corporate security risks.
Organizations frequently add employees, offices, facilities, vendors, technology, travel, events, and customers faster than their security programs evolve. A security strategy that worked effectively when a company had 50 employees and one location may no longer be appropriate after the organization expands to multiple offices, hundreds of employees, or a significantly larger operational footprint.
Growth can create questions that executives may not immediately consider:
Are access-control procedures and/or technologies still appropriate and relevant?
Are new facilities being evaluated for security vulnerabilities?
Have employee onboarding and termination procedures kept pace with growth?
Are security responsibilities clearly defined across locations?
Have new executives or employees created additional travel or protection requirements?
Are security standards consistent across facilities?
Has the organization’s emergency response plan been updated?
Security should evolve alongside the business. Organizations that wait until after an incident to reassess their security posture may discover that vulnerabilities have existed for months or even years.
A physical security assessment can help organizations identify these gaps and determine whether existing security measures remain appropriate as the business changes.
2. Overreliance on Security Policies and Procedures
Policies and procedures are important components of a corporate security program. However, having a policy does not necessarily mean an organization is prepared to execute it effectively.
Many organizations maintain emergency response plans, workplace violence policies, visitor-management procedures, evacuation plans, and incident-response protocols. The problem is that these plans may rarely—or never—be tested under realistic conditions.
Employees may not know their responsibilities. Managers may make conflicting decisions. Communication channels may become overwhelmed. Security personnel may discover that procedures written years ago no longer reflect current operations.
This creates an important distinction between security compliance and security effectiveness.
Executives should ask:
If this happened tomorrow, could our organization actually execute the plan?
Tabletop exercises, security drills, vulnerability assessments, and physical security red-team exercises can help identify gaps that aren’t apparent from simply reviewing documentation.
A security plan should not simply exist on paper. It should be tested, understood, and capable of working under pressure.
3. Third-Party and Vendor Security Risks
Organizations often invest significant resources protecting their own facilities and employees while overlooking security risks introduced by third parties.
Contractors, vendors, temporary workers, delivery personnel, property-management companies, event partners, and other external organizations may have legitimate access to facilities, sensitive areas, information, or employees.
The issue isn’t simply whether a vendor is trustworthy. The larger question is whether appropriate security controls are in place.
Executives should consider:
Who has access to company facilities?
Are contractor credentials removed when access is no longer required?
Are vendors subject to appropriate screening?
Are third parties aware of emergency procedures?
Are security expectations clearly defined in contracts?
Do vendors create additional risks during large-scale events?
Are former contractors promptly removed from access systems?
Third-party risk becomes particularly complicated when an organization assumes another party is responsible for security without clearly defining where responsibilities begin and end.
Organizations should understand the security implications of everyone who has access to their people, property, facilities, information, and operations.
4. Executive and High-Profile Personnel Exposure
Executives and other high-profile employees can face security risks that aren’t present for the average employee.
Travel, public appearances, conferences, corporate events, media exposure, social media activity, residences, and predictable routines can create opportunities for unwanted attention or targeted incidents.
However, executive security shouldn’t be viewed solely through the narrow lens of traditional executive protection.
A comprehensive approach considers the executive’s entire exposure environment.
For example, an executive traveling to an unfamiliar city may face substantially different risks than when attending a meeting at corporate headquarters. A public-facing executive speaking at a major conference may have different vulnerabilities than when working from a private office.
Organizations should consider:
Executive travel security
Event and venue security assessments
Advance planning
Transportation security
Residential security considerations
Public exposure and predictable routines
Threat monitoring and intelligence
Coordination with corporate security
Emergency response planning
The goal isn’t to unnecessarily restrict executives or disrupt their schedules. It is to understand their exposure and establish appropriate protective measures based on the actual risk environment.
5. Failure to Test the Physical Security Environment
One of the most overlooked security risks for businesses is assuming that physical security controls work simply because they are installed.
A camera system may provide extensive coverage but still contain blind spots. An access-control system may function properly from a technical standpoint while still allowing unauthorized individuals to exploit human behavior. A security officer may be positioned at an entrance but lack the information, training, or authority needed to respond effectively.
If someone wanted to gain unauthorized access to this facility, what would they try?
A properly designed physical security assessment evaluates the environment from the perspective of someone attempting to identify and exploit vulnerabilities.
Testing may identify issues involving:
Access control
Perimeter security
Employee security awareness
Visitor management
Security officer procedures
Surveillance coverage
Physical barriers
Emergency response
Sensitive areas
After-hours security
Communication procedures
The objective isn’t to criticize an organization’s security personnel or existing program. The objective is to identify opportunities for improvement before a real threat discovers them.
Turning Security Blind Spots Into Strategic Advantages
The most effective corporate security programs aren’t built around fear. They’re built around preparation, awareness, and risk management.
Executives don’t need to anticipate every possible threat. They need visibility into the risks that could materially affect their employees, facilities, reputation, customers, and business operations.
That requires leadership teams to periodically step back and ask difficult questions:
Where are our security vulnerabilities?
What assumptions are we making about our security program?
Have we actually tested those assumptions?
Has our security strategy kept pace with the organization?
Security assessments, vulnerability reviews, red-team exercises, executive security planning, and other proactive measures can help organizations identify weaknesses before they become costly incidents.
A Proactive Approach to Corporate Security
At Premier Risk Solutions, we help organizations take a proactive approach to security by evaluating vulnerabilities, identifying practical solutions, and helping leadership teams better understand their security risk environment.
Our approach is designed to help organizations move beyond simply having security policies and procedures toward developing a security program that is practical, measurable, and aligned with the organization’s overall risk profile.
Because the most dangerous security vulnerability isn’t always the one you can see.
Sometimes, it’s the one you haven’t thought to look for.
Is Your Organization Confident in Its Security Posture?
A proactive security risk assessment can help identify potential vulnerabilities before they become incidents.
If your organization is experiencing significant growth, opening a new facility, preparing for a major event, managing executive security concerns, or simply wants an independent evaluation of its existing security program, Premier Risk Solutions LLC can help.
Contact Premier Risk Solutions LLC to discuss how a proactive physical security assessment can help identify vulnerabilities and strengthen your organization’s security posture.
Physical Security Penetration Testing is a critical yet often underutilized component of an organization’s overall risk management strategy. While cybersecurity receives significant attention, many breaches still occur because attackers exploit physical access points, human behavior, or procedural gaps.
A physical security red team exercise provides organizations with a realistic, ethical, and controlled way to test their defenses against real-world threats. At Premier Risk Solutions LLC, we use structured red team methodologies to help clients identify vulnerabilities, validate controls, and strengthen security posture without disrupting operations.
This guide outlines a step-by-step red team exercise for physical security penetration testing, along with the key benefits organizations gain from this proactive approach.
What Is a Physical Security Red Team Exercise?
A Physical Security Red Team Exercise simulates the actions of an adversary attempting to gain unauthorized access to facilities, restricted areas, or sensitive assets. Unlike audits or checklist-based assessments, red teaming tests how people, processes, and technology perform together under realistic conditions.
The goal is not to embarrass staff or “beat” security—but to uncover risk before it can be exploited. It is an exercise to educate and learn, not a “gotcha” moment.
Step 1: Define Scope, Objectives, and Rules of Engagement
Every successful physical security penetration test begins with clearly defined parameters.
During execution, red team members attempt access using approved and pre-authorized techniques, which may include:
Testing employee challenge behavior
Evaluating access control enforcement
Observing guard response and escalation
Assessing adherence to visitor and escort policies
All activity is documented in real time. Professionalism and respect for employees and confidentiality are essential aspects throughout this phase.
Step 5: Evaluate Detection, Response, and Escalation
A core objective of physical red teaming is measuring how quickly and effectively threats are detected and handled.
Key observations include:
Whether suspicious behavior was noticed (and when it was)
How employees responded when challenged
Speed and effectiveness of security response
Consistency with documented procedures
This step often reveals gaps between policy and practice.
Step 6: Document Findings and Root Causes
Following execution, findings are compiled into a structured report focused on actionable risk reduction.
Reports typically include:
Timeline of events
Entry points tested and outcomes
Evidence (where pre-authorized)
Root cause analysis (training, process, or technology)
Risk ratings tied to business impact
The emphasis is on systemic improvement, not individual fault.
Step 7: Executive Debrief and Security Improvement Roadmap
The exercise concludes with a leadership debrief, translating technical findings into business-relevant insights.
Organizations receive:
Clear explanations of identified risks
Prioritized remediation recommendations
Guidance on policy updates and training
Support for security investment decisions
This ensures results lead to measurable improvement.
Benefits of Physical Security Red Team Penetration Testing
Real-World Validation
Red team exercises test controls as they are actually used—not as they are designed on paper.
Improved Employee Awareness
Staff gain clarity on when and how to challenge unfamiliar individuals, strengthening security culture.
Reduced Physical and Insider Threat Risk
Many incidents exploit trust and routine. Red teaming exposes these weaknesses safely.
Stronger Incident Response Capabilities
Organizations learn how effectively their teams detect, escalate, and respond to threats.
Executive-Level Visibility
Leadership gains objective data to guide risk management and compliance decisions.
Why Physical Security Red Teaming Matters
Physical security threats continue to evolve, and attackers often target the path of least resistance. Organizations that rely solely on policies or technology without testing them under realistic conditions remain exposed.
A well-executed physical security red team exercise provides clarity, confidence, and a roadmap for improvement—before a real incident occurs. At Premier Risk Solutions LLC, we help organizations move beyond assumptions and toward measurable, defensible security.
When organizations think about return on investment (ROI), the conversation often centers around revenue growth, operational efficiency, or technological innovation. Yet, one of the most overlooked sources of ROI comes from an area that directly affects every aspect of business continuity: Physical Security.
At Premier Risk Solutions LLC, we’ve seen firsthand how strategic physical security consulting helps organizations save money, protect people and assets, and maintain brand reputation—all while strengthening their overall risk posture. In today’s landscape of evolving threats, the question is no longer “Can we afford security consulting?” but rather, “Can we afford not to?”
Understanding the Value of Security Consulting
Physical security consulting is about more than installing cameras or hiring guards. It’s a holistic process that evaluates your environment, policies, procedures, staffing, and technology to create a customized plan that reduces vulnerabilities. The ROI comes not just in cost savings, but in risk avoidance and operational resilience.
Think of it this way: a single incident—whether a break-in , workplace violence event, or theft—can cost far more than the investment in professional security guidance. The role of a consultant is to anticipate these risks, design solutions to prevent them, and align security with organizational strategy.
Key Areas Where ROI Becomes Tangible
1. Cost Avoidance Through Risk Mitigation
Organizations often underestimate the financial impact of security incidents. Data from industry studies show that workplace violence incidents can cost companies millions in legal fees, lost productivity, and reputational damage. Theft or fraud can drain resources and erode trust.
By identifying weak points before they are exploited, security consulting helps avoid these high-cost disruptions. The ROI is clear: every prevented incident is money saved.
2. Operational Efficiency and Productivity
Poorly designed security measures can slow down operations. For example, inefficient access control systems frustrate employees and create bottlenecks. Consultants streamline these systems so security is effective without disrupting day-to-day business. The result? A safer workplace that actually enhances productivity.
3. Insurance and Compliance Savings
Many insurers reward companies that demonstrate strong security measures with lower premiums. Similarly, industries with regulatory requirements—such as finance, healthcare, or critical infrastructure—face steep fines for non-compliance. Security consulting ensures you meet or exceed standards, reducing financial liability while opening the door to cost savings.
4. Protecting Brand Reputation
In today’s digital-first world, news of a security breach spreads quickly. Beyond immediate financial losses, reputational damage can linger for years, impacting customer trust and investor confidence. Consulting services help businesses put proactive measures in place to ensure they are seen as reliable, safe, and trustworthy. That reputational stability is a long-term ROI few organizations can ignore.
5. Strategic Alignment With Business Goals
Security isn’t just a safety function—it’s a business enabler. When consultants design strategies that align with corporate objectives (such as supporting global expansion, safeguarding intellectual property, or protecting executives), the ROI extends beyond cost avoidance. Security becomes a foundation for growth.
Real-World Examples of ROI
Corporate Campus Security: A global tech company implemented consultant-recommended upgrades to access control and visitor management. The result was a 30% reduction in unauthorized access attempts, accompanied by measurable reductions in insurance premiums.
Executive Protection Programs: A consulting-led risk assessment for an executive travel program prevented multiple potential security incidents, saving the company both in liability exposure and reputational damage.
Retail Loss Prevention: Retailers who implemented consultant-guided physical and policy controls saw theft-related losses drop significantly, directly improving profit margins.
Why Now Is the Time to Invest
The threat landscape is evolving rapidly. From workplace violence and insider threats to supply chain disruptions and geopolitical risks, companies face more variables than ever before. At the same time, emerging technologies like AI-driven surveillance, smart access systems, and data integration are creating new opportunities for proactive protection.
Investing in physical security consulting now allows organizations to leverage these advancements strategically, ensuring they are not just reacting to threats but staying ahead of them.
The Bottom Line
The ROI of physical security consulting cannot always be measured in a single dollar figure, but its impact is undeniable. It prevents losses, strengthens compliance, improves efficiency, safeguards reputations, and supports long-term growth.
At Premier Risk Solutions LLC, our mission is to help clients recognize that security is not a cost center—it’s a value driver. By investing in professional consulting, organizations position themselves to thrive in an uncertain world. Reach out to us today to see how we may be of assistance!
In today’s hyperconnected and unpredictable global environment, corporate success is no longer driven by operations, marketing, and innovation alone. One element is often underestimated until it’s too late: security. Security is no longer just about locks, cameras, and badges (or guards, gates, and guns)—it’s a critical function that directly impacts your brand reputation, operational continuity, employee safety, and the organizational bottom line.
At Premier Risk Solutions LLC, we believe that security is not a support function—it’s a strategic one. Here’s why forward-thinking companies must embed security into the fabric of their corporate strategy.
1. The Threat Landscape Is Evolving
Gone are the days when security threats were limited to burglary or physical trespassing. Today’s organizations face multi-dimensional risks, including:
Crisis events such as pandemics, natural disasters, or geopolitical unrest
Each of these can cause significant financial, legal, and reputational damage. Security must now be anticipatory—not reactive—and that requires strategic placement at the leadership table.
A recent report by IBM showed that the average cost of a data breach in the U.S. exceeds $5 million. Yet many companies still treat security as an afterthought, addressing threats only after a breach or incident occurs.
2. Security Aligns with Enterprise Risk Management
Every company has risk on the radar—whether it’s financial, legal, operational, or reputational. Security intersects all these domains. If an executive is targeted abroad, or if a protest breaks out at a facility, how fast your team can respond depends on the level of preparedness embedded into your core operations.
When security is siloed from business strategy, risk management becomes fragmented. When it is integrated, your organization can build a resilient, agile framework capable of addressing both expected and unforeseen disruptions.
3. Protecting People = Protecting Performance
Your employees are your most valuable asset—and they’re also the most vulnerable during times of crisis. From workplace violence to executive protection during international travel, proactive security measures ensure that your team feels safe, supported, and focused.
Incorporating security into corporate strategy sends a message: “We take your safety seriously.” That enhances morale, retention, and your ability to attract high-caliber talent. It also reduces liability exposure in the event of an incident.
4. Investor Confidence and Board Expectations
Today’s investors and board members expect organizations to have robust, demonstrable plans in place for risk mitigation. Whether it’s cybersecurity, executive safety, or supply chain security, stakeholders want to know: What are you doing to prevent disruptions?
A company that integrates security into its strategic framework is better positioned to earn investor trust, secure funding, and weather periods of instability with minimal impact.
5. Reputation Management in the Age of Instant News
In the digital age, one poorly handled security incident can go viral and cause long-term brand damage. From data leaks to on-site incidents, how your company responds and communicates during a crisis can determine whether customers stay loyal or walk away.
When security is part of strategic planning, crisis communication protocols are already in place. Response teams are trained. Executives are briefed. And most importantly, the organization can respond swiftly, calmly, and with control—a key differentiator in moments of public scrutiny.
6. Security Adds Value—Not Just Cost
Too often, security is seen as a cost center. But when aligned with strategy, it becomes a value driver. Consider these examples:
A well-designed executive protection program allows leaders to focus on growth without distraction.
Threat assessments and travel security planning help your team expand into new markets safely.
Business continuity plans reduce downtime after natural disasters or supply chain disruptions.
Smart security investments pay dividends by preventing losses, safeguarding innovation, and maintaining customer trust.
Final Thoughts: Strategic Security Is Smart Business
Security is no longer just a department—it’s a business function that touches every level of an organization. From the C-suite to the front lines, your people, assets, and operations deserve strategic protection that scales with your goals.
At Premier Risk Solutions LLC, we partner with organizations to design and implement security solutions that are proactive, professional, and aligned with your business objectives. Whether you need executive protection, threat intelligence, or a full-scale risk assessment, we’re ready to help you turn security into a competitive advantage.
Is your security strategy where it needs to be? Let’s talk.